Be Obsessed
or Be Normal.
Blue-team operations, threat detection and incident response across enterprise environments. I design and operationalise the controls that keep critical infrastructure defensible — and hold up when someone actually tries.
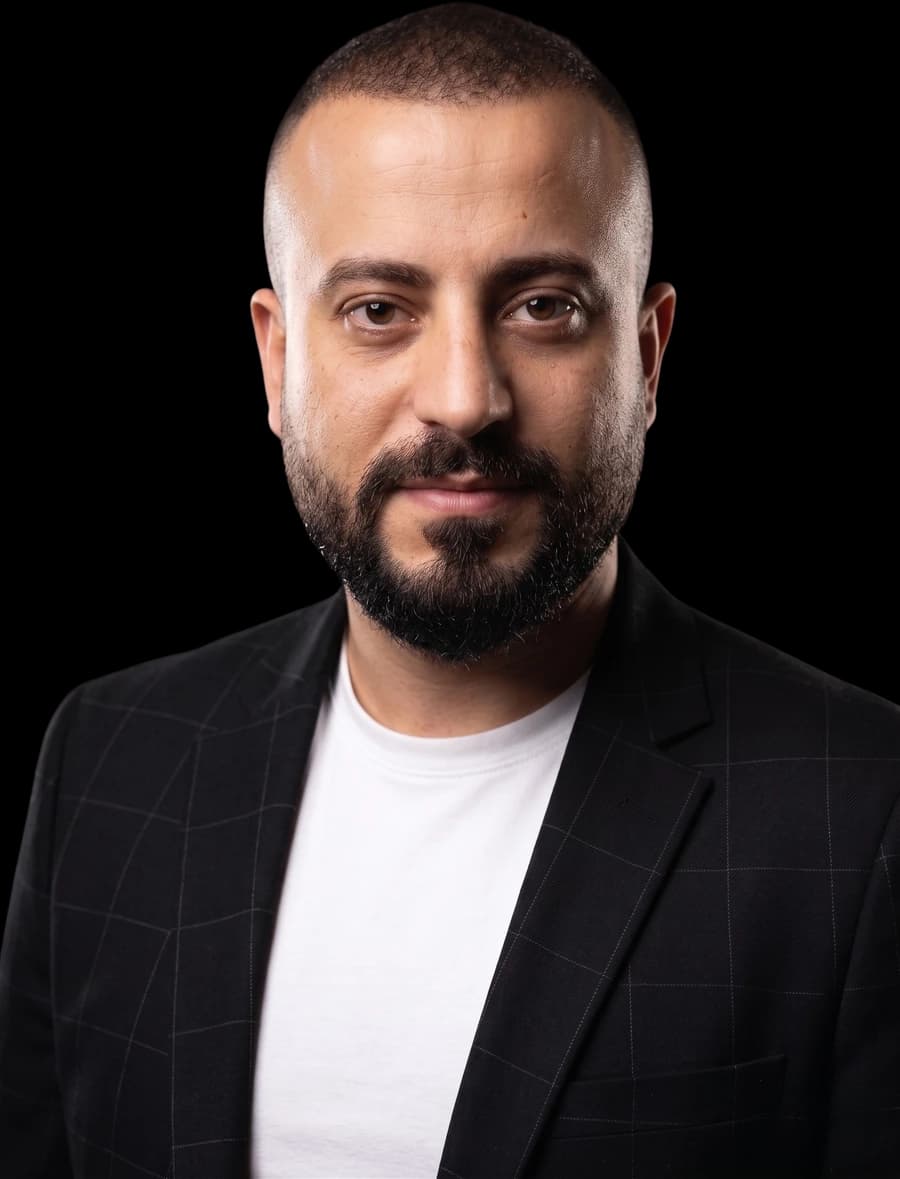
From frontline SOC analyst to leading a multi-tenant SOC — incident response, security engineering, and the data-protection controls underneath both. The discipline predates the career: national-level triathlon, still officiating.
SOC operations and security engineering across a multi-tenant MSSP portfolio — setting the strategy and running the execution behind threat detection, cyber defence and incident response.
End-to-end deployment and configuration of the Microsoft E5 Security Stack across Azure — endpoints, identities, cloud and email brought under one coverage model.
DLP policies and Insider Risk workflows that stop unauthorised exfiltration across cloud and endpoint channels — and the ISO 27001 risk register, audit-readiness documentation and executive reporting that sit above them.
Initial alert triage through containment, eradication and post-incident documentation, run across Sentinel and Defender XDR.
Notes on SOC operations and incident response, in English and Arabic. The first pieces are being written — the archive opens when there is something in it worth reading.
Tell me when it’s liveCurrently leading a SOC.
Open to the next hard problem.
Hiring for a blue-team role, weighing an MSSP, or stuck on a detection that will not stop firing — all three are worth an email.